Securing a Windows Active Directory environment is paramount for any organization, and a cornerstone of this security lies in the proper authentication and encryption mechanisms. Domain controllers, being the gatekeepers of user and computer authentication, require robust security measures to protect critical services like LDAP over SSL (LDAPS), Kerberos, and various other encrypted communications. Central to establishing this trust and facilitating secure communication is the Domain Controller Certificate Template, a specialized configuration within a Microsoft Certificate Authority (CA) that dictates the properties and issuance rules for certificates specifically designed for these crucial servers.
These certificates enable domain controllers to prove their identity to other systems, ensuring that clients are communicating with legitimate servers and preventing man-in-the-middle attacks. Without correctly configured certificates, essential services that rely on strong authentication and encryption may fail or operate in an insecure manner, leaving the Active Directory infrastructure vulnerable. Therefore, understanding and properly managing these templates is not just a best practice, but a fundamental requirement for maintaining a secure and functional AD environment.
The process involves more than just issuing a certificate; it necessitates a deep dive into the template’s properties, including cryptographic settings, extensions, and security permissions. Misconfigurations can lead to operational issues, authentication failures, or even security bypasses. This article will explore the intricacies of the domain controller certificate template, guiding you through its importance, configuration, and best practices for deployment and management within your Active Directory ecosystem.
The Critical Role of Domain Controller Certificates
Domain controller certificates play a foundational role in the security and functionality of an Active Directory environment. They are not merely an add-on but an essential component for several critical services and protocols. Understanding their purpose is the first step in appreciating the importance of their proper configuration.
Enabling Secure LDAP (LDAPS)
One of the most prominent uses for domain controller certificates is to enable LDAP over SSL (LDAPS). By default, LDAP communication is unencrypted, meaning credentials and other sensitive information are transmitted in plain text. LDAPS encrypts this traffic, protecting it from eavesdropping and tampering. For LDAPS to function, domain controllers must present a valid server authentication certificate issued by a trusted Certificate Authority. This certificate is tied to the domain controller’s hostname, ensuring that clients can verify they are communicating with the authentic server.
Kerberos Authentication Enhancements
While Kerberos is the primary authentication protocol in Active Directory, certificates can enhance its security, particularly in scenarios involving smart card logon. When users log on using smart cards, the Kerberos authentication process relies on certificates issued to the domain controllers for secure key exchange and authentication. These certificates establish trust between the smart card and the domain controller, crucial for secure smart card-based authentication.
IP Security (IPSec) and VPN Connections
Domain controller certificates can also be leveraged for IPSec in certain advanced configurations, securing communication channels between servers. Furthermore, if your network utilizes VPN solutions that integrate with Active Directory for authentication, domain controller certificates might be essential for the secure establishment of these VPN tunnels, ensuring the authenticity of the domain controller providing the authentication service.
Other Encrypted Communications
Beyond these core services, many other Active Directory-related applications and features may rely on encrypted communication with domain controllers. Whether it’s secure replication, communication with third-party applications, or specific management tools, the presence of a valid and trusted certificate on the domain controller ensures the integrity and confidentiality of these exchanges.
Understanding the Domain Controller Certificate Template
At the heart of issuing certificates to domain controllers is the Domain Controller Certificate Template. This template is a blueprint within a Microsoft Certificate Authority (CA) that defines all the parameters for certificates intended for domain controllers. It dictates everything from the certificate’s purpose and validity period to its cryptographic settings and the permissions required for issuance.
Default Domain Controller Templates
Microsoft CAs typically come with several built-in certificate templates. For domain controllers, two primary templates are relevant:

- Domain Controller: This template is used to issue certificates for domain controllers for various purposes, including secure LDAP and Kerberos authentication. It’s designed to provide server authentication and potentially client authentication capabilities.
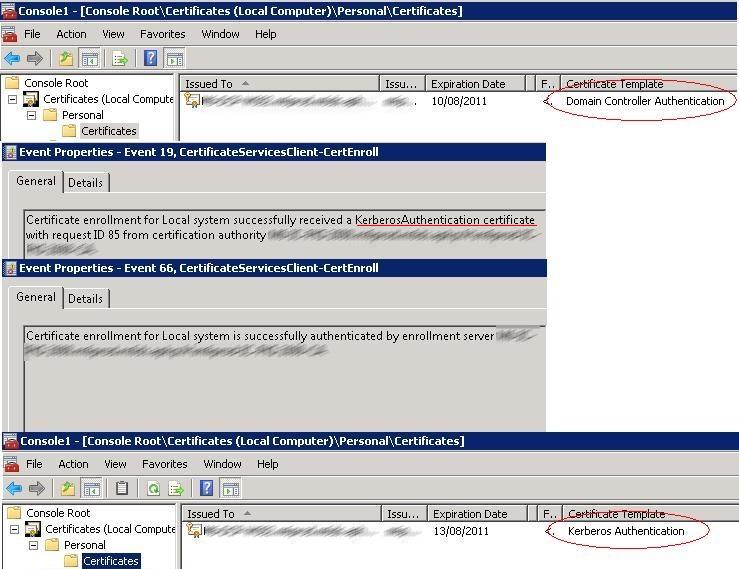
- Kerberos Authentication: A more specialized template, often used when specific Kerberos-related certificate requirements exist, particularly for smart card logon. It explicitly includes the Kerberos KDC Authentication Enhanced Key Usage (EKU).
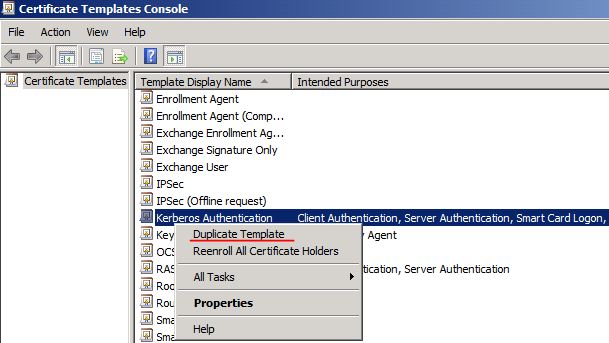
It’s a common and recommended practice to duplicate an existing template rather than modifying the default ones directly. This approach preserves the original template for future reference or in case of misconfiguration, and allows for custom settings tailored to your organization’s specific security policies. The “Domain Controller” template is frequently duplicated as a starting point.
Key Properties and Configuration of the Domain Controller Certificate Template
When configuring a Domain Controller Certificate Template, several critical properties must be correctly set to ensure the issued certificates function as intended and meet security requirements. These properties are accessed through the Certificate Templates Console on your CA.
Compatibility Settings
- Certification Authority: Choose the oldest CA version your environment supports. This ensures that certificates issued from this template are compatible with all your CAs.
- Certificate Recipient: Select the oldest operating system version that will be requesting certificates from this template. This impacts the cryptographic providers available and the features the certificate can support. For modern environments, Windows Server 2008 R2 or Windows Server 2012 R2 is often a good balance.
General Tab
- Template display name: A descriptive name for your custom template (e.g., “MyOrg Domain Controller Auth”).
- Validity period: How long the certificate will be valid (e.g., 2 years). Balance security (shorter validity) with administrative overhead (longer validity).
- Renewal period: How long before expiration the certificate can be renewed (e.g., 6 weeks).
Request Handling
- Purpose: Ensure “Signature and encryption” is selected.
- Allow private key to be exported: Generally, this should not be enabled for domain controller certificates, as it can compromise the private key.
- Renew with same key: Typically unchecked for domain controllers to ensure new key generation on renewal, enhancing security.
- For autoenrollment, do not automatically reenroll if a local certificate already exists: This is crucial. For domain controllers, you usually want to reenroll and get a new certificate when the existing one expires. Leave this unchecked to allow autoenrollment to manage renewals.
Cryptography
- Provider Category: Ensure “Key Storage Provider” is selected for modern cryptography.
- Algorithm: RSA is standard.
- Minimum key size: 2048 bits is the minimum recommended for RSA. 3072 or 4096 bits offer stronger security if supported by your infrastructure and performance needs.
- Request hash: SHA256 or higher (SHA384, SHA512) for strong hashing. Avoid SHA1.
Server Supersede Templates
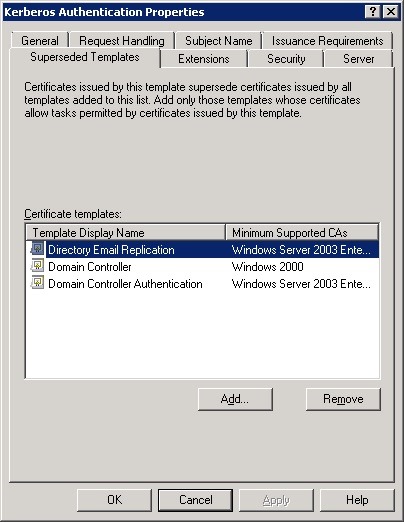
This tab allows you to specify which older templates this new template will replace. If you’re creating a new, improved domain controller template, you might want it to supersede the default “Domain Controller” or “Kerberos Authentication” templates. This ensures that domain controllers automatically migrate to the new template’s certificate when they renew.

Extensions Tab
This is one of the most critical sections.

-
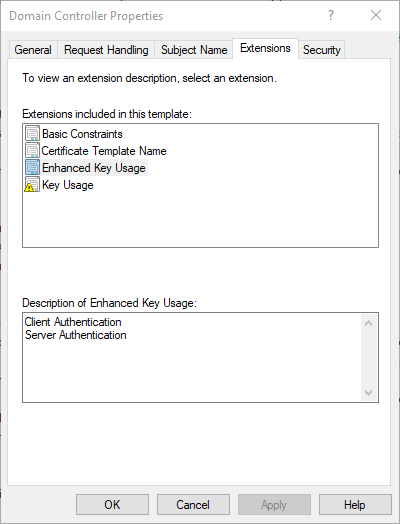
Application Policies (Enhanced Key Usage – EKU): This defines what the certificate can be used for. For domain controllers, the following EKUs are essential:

- Server Authentication (1.3.6.1.5.5.7.3.1): Absolutely required for LDAPS and proving the server’s identity.
- Client Authentication (1.3.6.1.5.5.7.3.2): Often included for mutual authentication scenarios, though not always strictly necessary for basic LDAPS.
- Kerberos Authentication (1.3.6.1.5.2.3.5): Essential for smart card logon scenarios and generally recommended for domain controllers.
- Directory Email Replication (1.3.6.1.4.1.311.21.19): Often present in the default template and useful for secure AD replication.
-
Subject Alternate Name (SAN): It’s highly recommended to include a SAN extension for domain controller certificates.
- Build from this Active Directory information: Check this.
- Include all subject alternative names: Check this.
- DNS Name: Essential to include the DNS name(s) of the domain controller. This ensures clients can validate the certificate regardless of how they address the DC (e.g., fully qualified domain name).
- Service principal name (SPN): Can be useful, especially for Kerberos, but less common than DNS name for the primary server authentication.

Security Tab
This tab controls who can request and enroll for certificates from this template.

- Domain Controllers (Group): This group must have Read and Enroll permissions. This allows domain controllers to automatically request certificates from this template.
- Enterprise Admins (Group): Should have Read, Write, and Full Control for managing the template itself.
- Cert Publishers (Group): Requires Read and Enroll permissions if you want delegated users or groups to be able to issue certificates manually.
- Authenticated Users: Should have Read permissions.
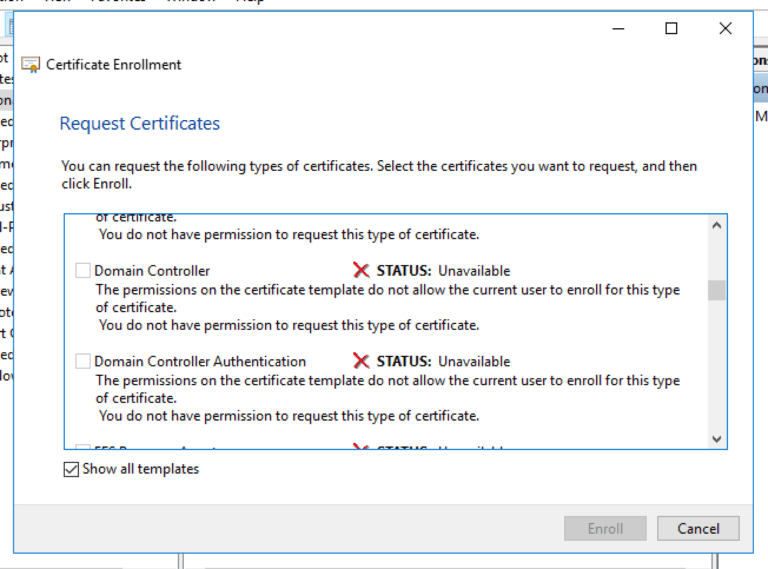
Ensure that the Domain Controllers group has the necessary permissions for autoenrollment to work correctly. Without “Enroll” permissions, domain controllers will not be able to obtain certificates from this template.

Modifying and Duplicating the Domain Controller Certificate Template
As mentioned, directly modifying built-in templates is generally discouraged. The recommended approach is to duplicate an existing template and then customize the copy.

Steps to Duplicate and Configure:
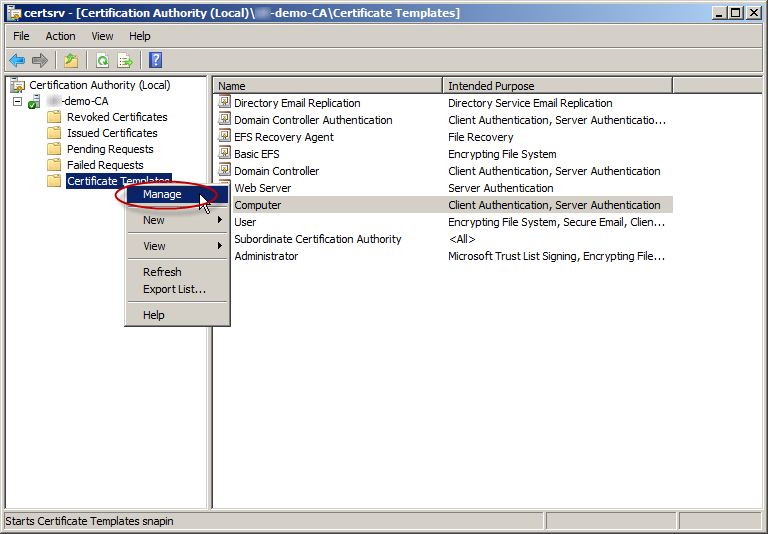
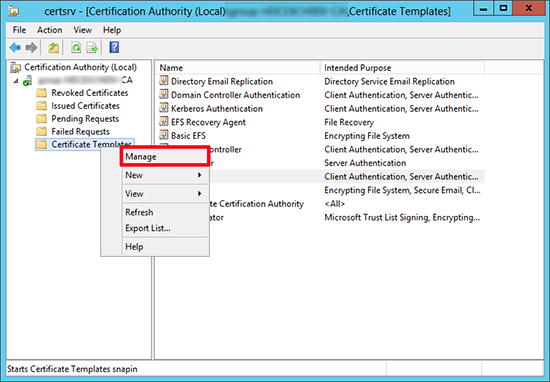
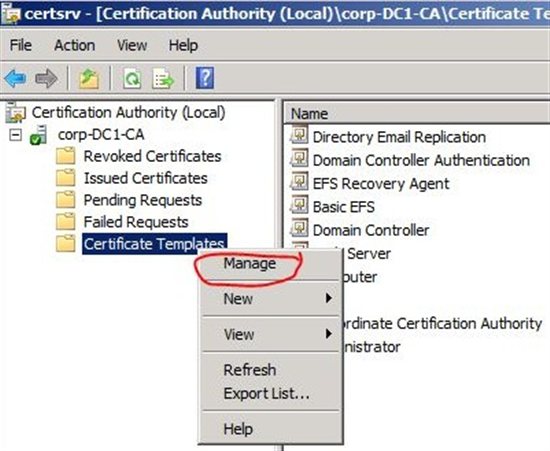
- Open Certificate Templates Console: On your CA, open
certtmpl.msc. - Duplicate a Template: Right-click on the “Domain Controller” template and select “Duplicate Template.”
- Choose Compatibility Settings: In the “Properties of New Template” window, set the Compatibility tab (CA and Recipient OS).
- Configure General Tab: Give it a unique “Template display name” (e.g., “MyOrgDCAuth”), set the validity and renewal periods.
- Adjust Request Handling: Verify “Purpose” and private key export settings.
- Review Cryptography: Set minimum key size and hash algorithm (e.g., 2048-bit RSA, SHA256).
- Define Server Supersede Templates (Optional but Recommended): On the “Superseded Templates” tab, click “Add…” and select the original “Domain Controller” template. This ensures that new certificates issued from your custom template replace the old ones.
- Set Extensions: Carefully configure the Application Policies (EKU) and Subject Alternate Name (SAN). Ensure Server Authentication, Client Authentication, and Kerberos Authentication EKUs are present, and that DNS Name is built from AD information.
- Configure Security Permissions: On the Security tab, grant
Read,Enroll, andAutoenrollpermissions to the Domain Controllers security group. Also, grantReadandEnrollto theEnterprise Domain Controllersgroup if it exists and is relevant in your environment. GrantRead,Write, andFull ControltoEnterprise Adminsand any other administrative groups responsible for managing templates. - Publish the Template: After configuring all properties, click “OK.” Then, on your CA, open the “Certification Authority” console (
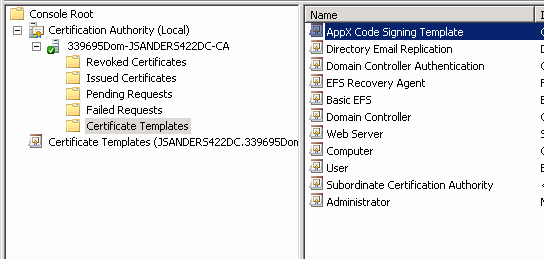
certsrv.msc). Right-click on “Certificate Templates,” select “New,” and then “Certificate Template to Issue.” Choose your newly created template and click “OK.”
Once published, your domain controllers will be able to request certificates based on this new template, particularly through autoenrollment.
Deploying Certificates to Domain Controllers via Autoenrollment
The most efficient and scalable way to deploy certificates to domain controllers is through autoenrollment, driven by Group Policy. This process leverages the permissions configured in the Domain Controller Certificate Template to automatically request, receive, and renew certificates without manual intervention.
Configuring Group Policy for Autoenrollment
- Create or Edit a GPO: Open the Group Policy Management Editor (
gpmc.msc). Create a new GPO or edit an existing one that is linked to the Domain Controllers Organizational Unit (OU). - Navigate to Public Key Policies: Go to
Computer Configuration->Policies->Windows Settings->Security Settings->Public Key Policies. - Enable Certificate Services Client – Auto-Enrollment: Right-click on “Automatic Certificate Request Settings” or “Certificate Services Client – Auto-Enrollment,” and select “Properties.”
- Configure Autoenrollment:
- Set the Configuration Model to Enabled.
- Check Renew expired certificates, update pending certificates, and remove revoked certificates.
- Check Update certificates that use certificate templates. This is crucial for domain controllers to enroll for the new template if it supersedes an older one.
- Apply and Verify: Link the GPO to the “Domain Controllers” OU. After Group Policy refreshes on the domain controllers (usually within 90 minutes, or immediately with
gpupdate /force), they will attempt to autoenroll for the new certificate.
Verification Steps
After deployment, verify that domain controllers have successfully received their certificates:
- Check Event Logs: On a domain controller, open Event Viewer and navigate to
Applications and Services Logs->Microsoft->Windows->CertificateServicesClient-AutoEnrollment. Look for events indicating successful certificate enrollment (Event ID 64). - Check Certificate Store: Open
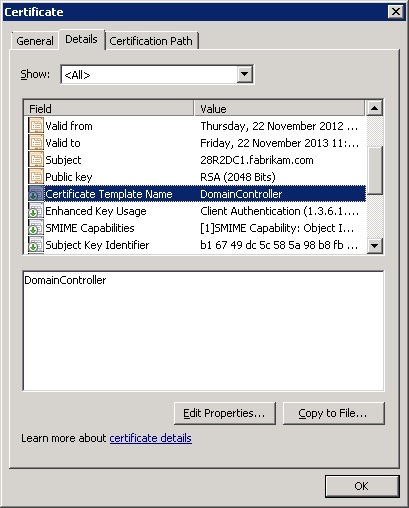
certlm.msc(Local Computer Certificates) on a domain controller. Navigate toPersonal->Certificates. Verify that a new certificate with the correct template name, validity, and EKUs has been issued. - Test LDAPS: Use tools like
ldp.exeto connect to a domain controller over port 636 and verify that the connection is successful and encrypted. Ensure the correct certificate is being presented.
Best Practices for Managing Domain Controller Certificates
Effective management of domain controller certificates extends beyond initial deployment. Adhering to best practices ensures ongoing security and operational stability.
Regular Auditing and Monitoring
- Monitor Certificate Expiry: Implement monitoring solutions to alert you well in advance of certificate expiration dates. This prevents service outages caused by expired certificates.
- Audit Certificate Issuance: Regularly review your CA logs for certificate issuance and revocation events. Ensure only authorized entities are requesting and receiving certificates.
- Check Domain Controller Health: Use tools like
dcdiagto monitor domain controller health, which often includes checks for valid certificates.
Secure Key Management
- Protect the CA: The Certificate Authority itself is a critical asset. Ensure it is highly secure, physically and logically protected, and that its private key is protected (e.g., using a Hardware Security Module – HSM).
- Strong Cryptography: Always use modern, strong cryptographic algorithms (e.g., RSA 2048-bit or higher, SHA256 or higher). Regularly review industry standards for updated recommendations.
Template Management
- Version Control: Document all changes made to your Domain Controller Certificate Template. Maintain version control for your custom templates.
- Supersede Old Templates: When creating new templates with improved security or updated settings, ensure they supersede older, less secure templates to facilitate automatic migration.
- Remove Unused Templates: Unpublish and remove any certificate templates that are no longer in use or are deemed insecure to minimize the attack surface.
Redundancy and High Availability
- Redundant CAs: For large or critical environments, deploy redundant CAs to ensure certificate issuance remains available even if one CA fails.
- CA Backup and Recovery: Implement a robust backup and recovery strategy for your CA, including its database and private key.
Conclusion
The Domain Controller Certificate Template is a cornerstone of Active Directory security, enabling critical functions like secure LDAP, Kerberos authentication, and various encrypted communications. By meticulously configuring this template, organizations can ensure that their domain controllers are equipped with robust, trusted identities, significantly enhancing the overall security posture of their Active Directory environment.
Understanding each property, from compatibility and cryptographic settings to application policies and security permissions, is vital for a successful implementation. Leveraging autoenrollment through Group Policy streamlines deployment and renewal, minimizing administrative burden and reducing the risk of certificate-related outages. Adopting best practices for auditing, monitoring, and template management further solidifies the security and reliability of your certificate infrastructure. In an era where cybersecurity threats are constantly evolving, the proper management of domain controller certificates is not just a recommendation but a fundamental necessity for protecting your most critical authentication services.
]]>


Related posts of "Domain Controller Certificate Template"
